1. Introduction
In the next few parts of this series, we look at various signature schemes and prove their security in the RO model. This part is dedicated to the analysis of Pointcheval and Stern Generic Signature Scheme of which the Schnorr scheme is an example. The generic scheme is built around a single  pair. Later parts of this series will focus on ring signature schemes. Ring signatures embed the actual signer in a ring of other possible signers to hide her identity. We will discuss them in parts 3, 4, 5, 6, and 7.
2. Pointcheval and Stern generic signature scheme
For a given message  , our generic scheme creates a signature
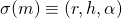 where
 is a random element chosen from a pre-defined set,
 (i.e., RO output on query
 ), and
 is fully determined by
 and
 . By design, we require that the probability of selecting any particular be upper-bounded by
 for a given security parameter
 .
Schnorr’s signature scheme is an example that fits this generic model. To see why, recall that  chooses a random commitment
 where
 is a pre-defined prime number. It then assigns
 where
 denotes a chosen generator of
 . Afterwards, is set to
 . Finally, is calculated as
 where
 denotes the signer’s private key. Note that can be any element of and so the probability that it takes on a specific value is equal to
 . By design, we choose the security parameter
 . This choice of guarantees that the aforementioned probability is upper-bounded by
 .
3. Security analysis – Unforgeability vis-a-vis EFACM
For unforgeability proofs, we follow the 5-step approach mentioned in part 1 of this series.
Step 1: To prove that this generic scheme is secure against EFACM in the RO model, we proceed by contradiction and assume that there exists a PPT adversary  such that:
 non-negligible in k).
Step 2: Next, we build a simulator  such that it:
- Does not have access to the private key of any signer.
- Has the same range as
 (i.e., they output signatures taken from the same pool of potential signatures over all possible choices of RO functions and respective random tapes and
 ).
- Has indistinguishable probability distribution from that of over this range.
is specific to the particular instance of the generic scheme being used. In what follows, we build a simulator for the case of a Schnorr signature.
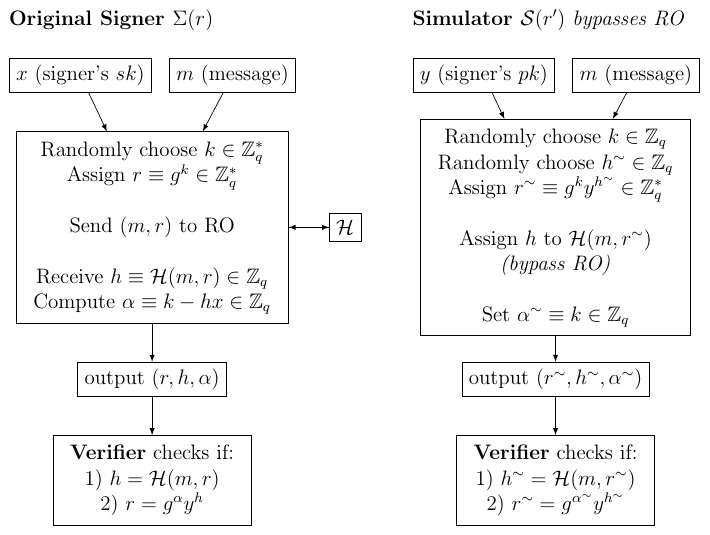
By construction, the output of  will satisfy the verification equations. Moreover, it assigns a random value for and bypasses the RO in doing so. Next, note the following:
- does not use any private key.
- and both have a range
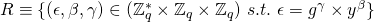 .
- and have the same probability distribution over
 . Indeed,
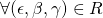 we have:
- For


- For


- For
With adequately built for the Schnorr scheme, we conclude that (refer to section 6 of part 1 of this series for a justification):
 non-negligible in k).
Step 3: We now show that the probability of faulty collisions is negligible (refer to section 6 of part 1 of this series for a description of collision types). The 2 types of collisions fo the generic scheme are:
 : A tuple that encounters — it makes its own random assignment to and bypasses RO — also appears in the list of queries that
 sends to RO. A conflict in the 2 values will happen with overwhelming probability and the execution will halt.
 : A tuple that encounters — it makes its own random assignment to — is the same as another tuple
 that encountered at an earlier time instance — here too, would have made its own random assignment to
 . Since the 2 tuples are identical (i.e.,
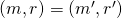 ), it must be that the 2 random assignments match (i.e.,
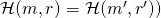 . With overwhelming probability, the 2 values will be different and the execution will halt.
The aforementioned collisions must be avoided. In order to do so, we first calculate the probability of their occurence. We assume that during an EFACM attack, can make a maximum of  queries to RO and a maximum of
 queries to . and are both assumed to be polynomial in the security parameter , since the adversary is modeled as a PPT Turing machine.

![Q_S\ queries\ to\ \mathcal{S}\ and\ Q\ queries\ to\ RO\}}]](https://delfr.com/wp-content/ql-cache/quicklatex.com-d8174849039a46a5deff31f0ffaa74a2_l3.png "Rendered by QuickLaTeX.com")


![\mathcal{S}\ and\ k^{th}\ queries\ to\ RO\}}]](https://delfr.com/wp-content/ql-cache/quicklatex.com-7561759e0f5278ba6c15285e4c0b67b5_l3.png "Rendered by QuickLaTeX.com")

![\mathcal{S}\ and\ k^{th}\ queries\ to\ RO]](https://delfr.com/wp-content/ql-cache/quicklatex.com-4eaa420f2f83cc41c35bcb51b6cb2746_l3.png "Rendered by QuickLaTeX.com")

 and are polynomial in , we conclude that
 is negligible in .
Next, we compute  :

![some\ of\ the\ queries\ to\ \mathcal{S} \}}]](https://delfr.com/wp-content/ql-cache/quicklatex.com-a963ab48af039f37a5c31a2b739c90a7_l3.png "Rendered by QuickLaTeX.com")

![2\ queries\ to\ \mathcal{S} \}}]](https://delfr.com/wp-content/ql-cache/quicklatex.com-7c943b2068a5dff5bee1a31cfa8ce91a_l3.png "Rendered by QuickLaTeX.com")

 is also negligible in . We then have:

 (negligible in k).

 , (non-negligible in )
Step 4: In this step, our objective is to show that if  is a successful tuple that generated a first EFACM forgery, then the following quantity is non-negligible in :


![and\ (\rho_{i} = \rho^{*}_{i})\ for\ i \in \{{1,...\beta -1\}}]](https://delfr.com/wp-content/ql-cache/quicklatex.com-cdddc2a12414ee6d024a00599fc4d122_l3.png "Rendered by QuickLaTeX.com")
Here  is an appropriate index that we will define in the proof. And to further simplify the notation, we let
 and
 . (
 and
 denote respectively the
 query to
 and
 ) for all
 .
Let’s take a closer look at  .
Any successful forgery must pass the verification test. One of the verification equations is to check if . So we distinguish between 2 scenarios (w.l.o.g. we assume that all -queries sent to RO are distinct from each-other since can keep a local copy of previous query results and avoid redundant calls):
- Scenario 1: was successful in its forgery, and no collisions occured, and it never queried RO on input .
- Scenario 2: was successful in its forgery, and no collisions occured, and it queried RO on input during its execution.
The probability of scenario 1 is upperbounded by the probability that picks a value for that matches the value of . Here, is the value that RO returns to  (the verification algorithm) when verifying the validity of the forged signature. (It is upper-bounded because at the very least, the constraint
 must be observed for a valid signature). And since can be any value in
 , we get:
 , (negligible in ).
So we assume that a successful forgery will likely be of the Scenario 2 type. We have:


 , (non-negligible in )
We then define  to be the index of the query sent by to RO during execution. We let
 if the query was never asked by . This definition allows us to build the following sets:
-
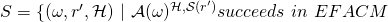
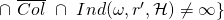
In other terms,
 is the set of tuples
 that yield a successful EFACM forgery when no collisions occur, and when queried RO on input at some point during its execution (i.e., scenario 2).
-
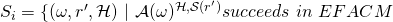
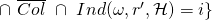
In other terms,
 is the set of tuples that yield a successful EFACM forgery when no collisions occur, and when the index of the -query on input sent to RO is equal to
 .
Recall that,  , which is non-negligible in .
And  partitions . So
 .
This implies that  .
If this were not the case, then one would get the following contradiction:
 .
So we introduce the set  consisting of all indices that meet the
 threshold, i.e.

We claim that  .
Proof: By definition of the sets we have:


The next step is to apply the splitting lemma to each  . First note that:


Referring to the notation used in the splitting lemma (section 7 of part 1), we let:
 ,
 ,
 ,
 ,

 is defined as the space of tuples of all random tapes
 , all random tapes , and all possibe RO answers to the first
 queries sent by .
 is defined as the space of all possible RO answers to the last
 queries sent by . The splitting lemma guarantees the existence of a subset
 of tuples such that:

 , we have

 , and so


We would like to compute the probability of finding a  successful tuple
 given that was a successful
 tuple and s.t.
 . That means finding the following probability:
 .
From the splitting lemma results, we have a (non-negligible in ) lower-bound on  .
Note however, that  and
 are generally distinct sets. And so we cannot conclude that

and therefore we cannot conclude that the following quantity is non-negligible in
In order to show that the above quantity is non-negligible in , we proceed differently. Suppose we can show that the following probability is non-negligible in :

This would imply that with non-negligible probability, we can find a tuple that belongs to  (and hence corresponds to a successful forgery) and at the same time belongs to
 . We can then invoke the splitting lemma result just mentioned, to find a second tuple coresponding to a second forgery and that has the desired properties.
To prove the above, we proceed as follows:


 , (since the ‘s are disjoint).


 , (
 result of splitting lemma above)
 (by the claim proven earlier)

And so we conclude that:


 , (non-negligible in ).
So let be such an index and such a tuple. From the result above, we know that finding such a  can be done with non-negligible probability. And since
 , we must have
 . We can then invoke the consequence of the splitting lemma, and write:


![= \rho_{\beta-1}^{*})] \geq \frac{\nu(k)}{4Q}](https://delfr.com/wp-content/ql-cache/quicklatex.com-21538cf1af2c2afa39506080e935dd89_l3.png "Rendered by QuickLaTeX.com")
We still have one last constraint to impose and that is that  . We show that the following quantity is non-negligible:

To prove this, note that if  and
 are independent events, then we can write:


And so we get  . This results allows us to write:


 (because we chose

 , (non-negligible in ).
Step 5: The final step uses the 2 forgeries obtained earlier to solve an instance of the Discrete Logarithm (DL) problem. Here is a recap of Step 4 results:
- With non-negligible probability of at least
 we get a successful tuple
 , s.t.
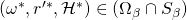 for some index
 . So by running a number of times polynomial in , we can confidently find such a tuple.
- Once we find such a tuple, we’ve also shown that with non-negligible probability of at least
 , we can find another successful tuple
 such that
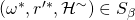 and
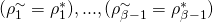 , but
 .
W.l.o.g, let correspond to  , and correspond to
 .
Recall that is the index of the query  that sends to the RO. Since the 2 experiments corresponding to the 2 successful tuples have the same random tapes
 and
 , and since the 2 corresponding ROs
 and
 behave the same way on the first
 queries, we can be confident that the first queries sent to the 2 ROs are identical. In particular the two
 queries are the same (i.e.,
 . Moreover by design,
 .
So we have 2 successful forgeries and  , with
 . Since both are valid signatures, they must satisfy the verification equations. For the particular case of a Schnorr signature scheme , they must satisfy the following 2 equations (1 verification equation per signature):
 , where
 is the public key of the signer whose signature is forging.
 , where is the public key of the signer whose signature is forging.
Writing  ( is the secret key of the signer whose signature is forging), we get:
 .
Since, , we can solve for (the DL of ) in polynomial time. This contradicts the intractability of DL on multiplicative cyclic groups and we conclude that our signature scheme (in this case the Schnorr’s scheme) is secure against EFACM in the RO model.
References
[1] D. Pointcheval and J. Stern. Security arguments for digital signatures and blind signatures. Journal of Cryptology, 2000.
Tags: Correctness, Privacy, Schnorr, Security, Signature, Unforgeability
No comments
Comments feed for this article
Trackback link: https://delfr.com/pointcheval-stern-generic-signature-scheme-monero-part-2-10/trackback/